On-Chain Money Laundering Is Evolving. Detection Needs to Keep Up.
In February 2025, approximately $1.5 billion was stolen from Bybit. Within minutes, the funds were swapped on a DEX, moved across chains via THORChain, mixed into memecoin transactions, and funneled into a centralized exchange. At no single point in that flow could address-based detection alone catch what was happening.
Lambda256 and Seoul National University's blockchain research group, Decipher, published a research report that confronts this problem head-on.
How On-Chain Money Laundering Has Evolved
Modern on-chain laundering no longer relies on a single technique. Based on real cases, here are the key laundering methods observed:
Privacy Protocols (Tornado Cash, Railgun)
Deposits and withdrawals are split into fixed denominations, making it cryptographically impossible to map a deposit address directly to a withdrawal address.
Cross-Chain Swaps (THORChain)
By switching both the chain and the asset simultaneously — for example, from Ethereum to Bitcoin — the method of analysis itself gets disrupted.
Memecoin Transactions
Value can be transferred through price and liquidity mechanics without any direct on-chain transfer. In the Bybit hack, a portion of the stolen funds showed signs of connection to addresses linked to Pump.fun-based memecoin issuers.
PerpDEX Profit/Loss Separation
One address takes the loss, another collects the gain — with no direct on-chain transfer between them. In the Radiant Capital hack, approximately $1.67 million was effectively laundered through Hyperliquid using this method.
NFT High-Value Transactions
NFTs from the same collection were purchased at prices over 153x above market value to transfer funds. In the Bittensor hack, funds passed through Railgun before being linked to Killer GF NFT transactions.
Individually, each transaction looks like normal on-chain activity.
Why Address-Based Detection Isn't Enough
On-chain data is public — but the existence of a transaction record and the ability to clearly see a criminal flow are two very different things. Here's what makes detection structurally difficult:
- A single incident may involve a theft address, swap address, bridge address, mixer deposit address, withdrawal candidate address, NFT transaction address, and CEX deposit address — all different
- After passing through a privacy protocol, the direct link between deposit and withdrawal is cryptographically cut
- When the chain changes, the address format, data structure, and analysis methodology all change at once
- Value transfers through NFTs, memecoins, and PerpDEX positions don't appear in transfer graphs
The risk isn't in any single address. It lives across multiple addresses, protocols, chains, and behavioral patterns.
FRAML: Treating Fraud and AML as One Incident
FRAML is a methodology that integrates fraud detection (FDS) and anti-money laundering (AML) into a single risk flow rather than treating them as separate functions.
In an on-chain environment, the distance between Fraud and AML is extremely short. An incident that begins with a hack or phishing attack can move through swaps, bridges, and mixers into an exchange within minutes. The anomalous withdrawal event that FDS needs to detect converts almost immediately into the money laundering flow that AML needs to track.
The core of FRAML isn't asking "is this transaction suspicious?" — it's asking "what incident is this fund flow progressing toward?" It connects the initial risk signal to the fund movement path, the protocols used, and the off-ramp, treating all of it as a single incident.
CLAIR FRAML: Putting On-Chain FRAML Into Practice
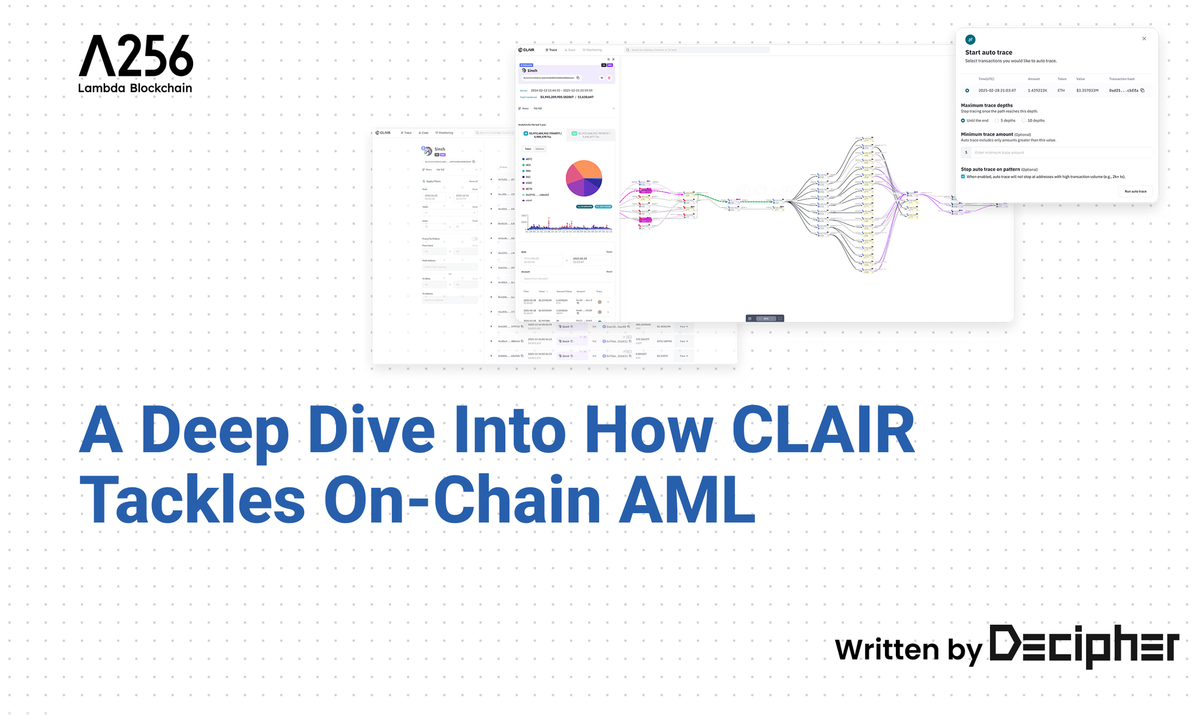
CLAIR FRAML applies this approach to a real operational environment, connecting detection, analysis, response, and reporting into one continuous flow.
Detection: Rule-based and watchlist-driven anomaly identification, alert severity and priority classification
Analysis: Multi-hop fund flow tracing, address and transaction risk scoring
Monitoring: Pre-transaction risk controls (Pre-TX) and post-transaction continuous screening (EDCS)
Reporting: Evidence base for STR filing, AI-assisted report generation
Using an ontology-based data structure and knowledge graph, CLAIR FRAML reconstructs fund flows that move across multiple addresses and chains into a single, coherent incident view.
What This Means for Financial Institutions
With the approval of Bitcoin spot ETFs, the expansion of stablecoin payments, and the growth of RWA tokenization, the reach of on-chain financial crime now extends well beyond exchanges — into banks, payment infrastructure, and custodians. Funds stolen from an exchange can flow through CEXs and OTC desks into bank accounts, triggering AML, STR, and sanctions risks along the way.
The time has come to evolve detection frameworks — from identifying individual suspicious transactions to understanding the full arc of an incident.
For a detailed breakdown of on-chain laundering techniques, fund flow tracing across the Bittensor, Radiant Capital, and Bybit incidents, and the analytical architecture behind CLAIR FRAML, download the full report on our resources page.
About Lambda256
Lambda256 is a blockchain technology company established in 2019, originating from Dunamu's blockchain research division. Built around Nodit, an enterprise-grade Web3 infrastructure platform; CLAIR, an ontology-based blockchain intelligence solution; and SCOPE, an institutional stablecoin integration platform, Lambda256 leads the commercialization of blockchain technology and the development of financial data ecosystems for global markets.
Contact us: www.lambda256.io